

Technical maintenance — Security patches
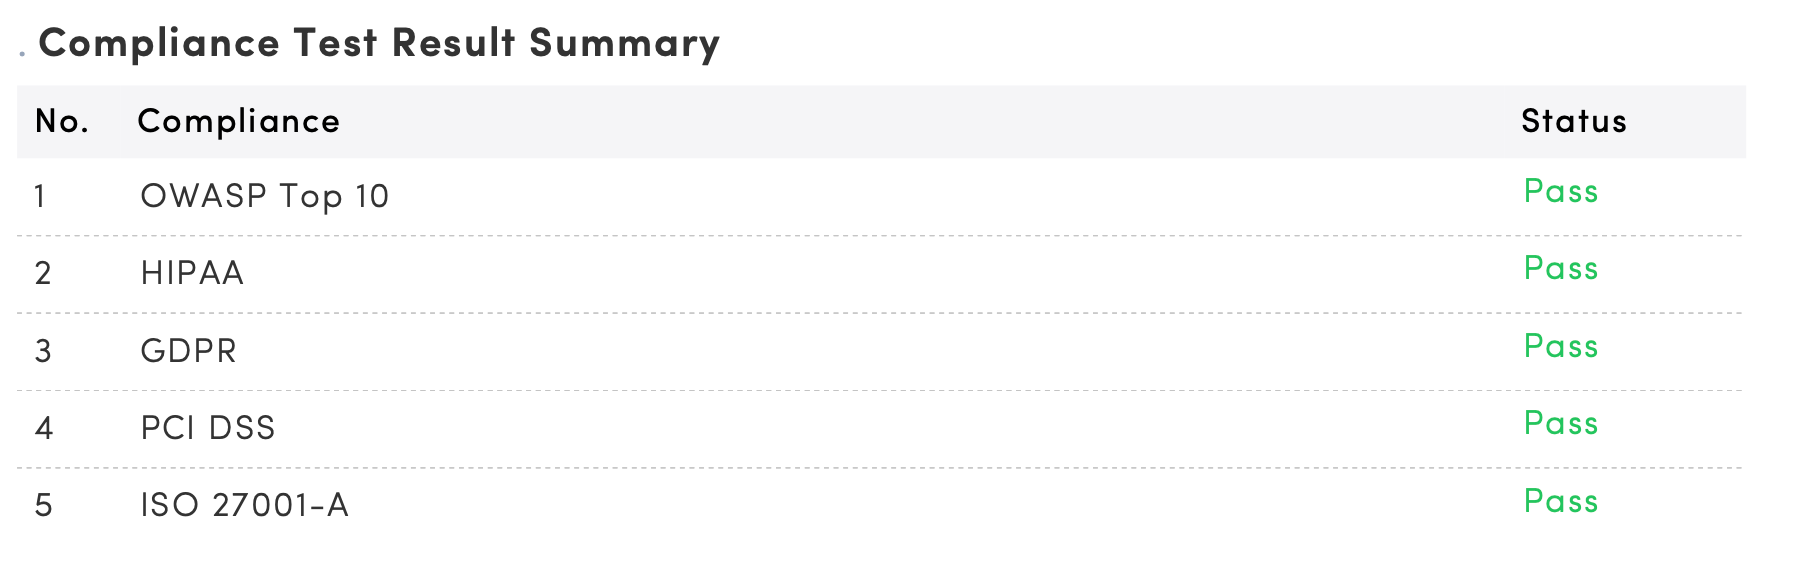

A number of security improvements were applied to keep Spendle in line with current security standards. Below is an overview of the technical changes.
Stronger encryption (TLS)
Section titled “Stronger encryption (TLS)”The infrastructure was updated to use modern encryption:
- Old and vulnerable cipher suites have been disabled.
- Only modern encryption (AES-GCM / ChaCha20) is permitted.
- Outdated TLS versions are no longer accepted.
In Spendle this aligns with current best practices for transport encryption. If an outdated browser is used, it may need to be updated to continue using Spendle.
Stricter browser security headers
Section titled “Stricter browser security headers”The HTTP response headers have been further tightened, including:
- Content Security Policy (CSP)
- Strict Transport Security (HSTS)
- Protection against MIME-sniffing and clickjacking
These headers contribute to protection against Cross-Site Scripting (XSS), unintended content injection and unsafe downgrade scenarios.
Stronger passwords
Section titled “Stronger passwords”When creating or changing the administration password, a strong password is now explicitly enforced.
Library updates
Section titled “Library updates”In addition to infrastructure and application changes, the libraries in use were updated to recent versions.
Test result
Section titled “Test result”After the changes, Spendle was tested against common security guidelines.